For the new user provisioning project, modifying group membership is one of the core objectives that must be met as those membership provides access to file shares and distribution groups, etc. This post will detail how to properly add a user to group membership with AD module command line.
In my hybrid lab environment, there are three types of groups that I have created for on boarding. I believe these are very basic and common group structure.
The following groups are evaluated:

1.Baseline groups (Groups meant for ALL new users in the company - ex: VPN access group)

2.Departmental groups (Groups meant for all new users in a specific department - ex: departmental file share access)

3.Custom groups (Groups listed as selection during new hire setup. ex: Distribution list, cross departmental access, application access, group policy members etc..)
Commands
On premise group type created using Active Directory Users & Computers (ADUC) or Active Directory Administrative center (ADAC) are:
* Security groups
* Distribution groups

Add users to those groups with the following command:

Add-ADGroupMember -Identity "Group name" -Members "User UPN"
On premise group type created using exchange admin center (EAC) are: (default scope is universal)
* Security groups (Mail enabled)
* Distribution groups
** Dynamic Distribution groups (Their memberships are determined automatically by filters. If a user is missing from a dynamic group, you must update the user's Active Directory attributes)

Add users to those groups with the following command:

# Add-DistributionGroupMember can be used for on premise or on cloud groups #

Add-DistributionGroupMember -Identity "Group Name or Email" -Member "User Name or Email"

Or

Add-ADGroupMember -Identity "Group SAM name" -Members "User UPN"
Verify:
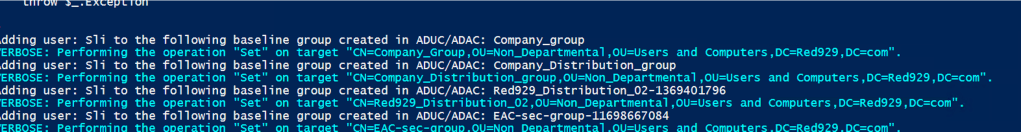
The following sample script adds user to group. Do note that “Add-ADGroupMember” can be used for EAC objects ONLY if the identity value is SAM account name.
try {
    #Establish an array for each item

    $Baseline_groups_AD=@(
    "Company_group",
    "Company_Distribution_group",
    "Red929_Distribution_02-1369401796",
    "EAC-sec-group-11698667084")

      foreach($item in $Baseline_groups_AD){
        # Add user to AD group

        Write-Output "Adding user: $UPN to the following baseline group created in ADUC/ADAC: $item"
        Add-ADGroupMember -Identity $item -Members $UPN -Verbose
    }

}catch{
    # get terminating error
    Write-Error -message $_.Exception
    throw $_.Exception
}
Troubleshoot:
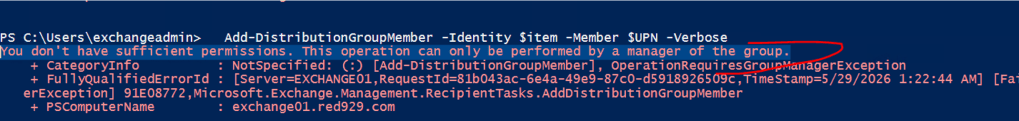
If using EAC command such as “Add-DistributionGroupMember “, EAC requires admin to be owner of the group that it is trying to modify. Either assign owner to the group or assign the role of [Organization Management] to service account.
Organization Management: This is the “Global Admin” equivalent for Exchange. Members have full, unrestricted access to the entire Exchange organization, allowing them to manage every type of group (Distribution, Dynamic, and Mail-Enabled Security Groups).

